The Firewall tab is used to allow or deny traffic between interfaces and networks, and to protect the KonnectOS System against excessive HTTP/HTTPS requests (DoS). It contains two collapsible sections, Firewall Rules and DoS; click the –/+ button of a section to collapse or expand it.
Select Security from the side menu bar. The Firewall tab is selected by default.
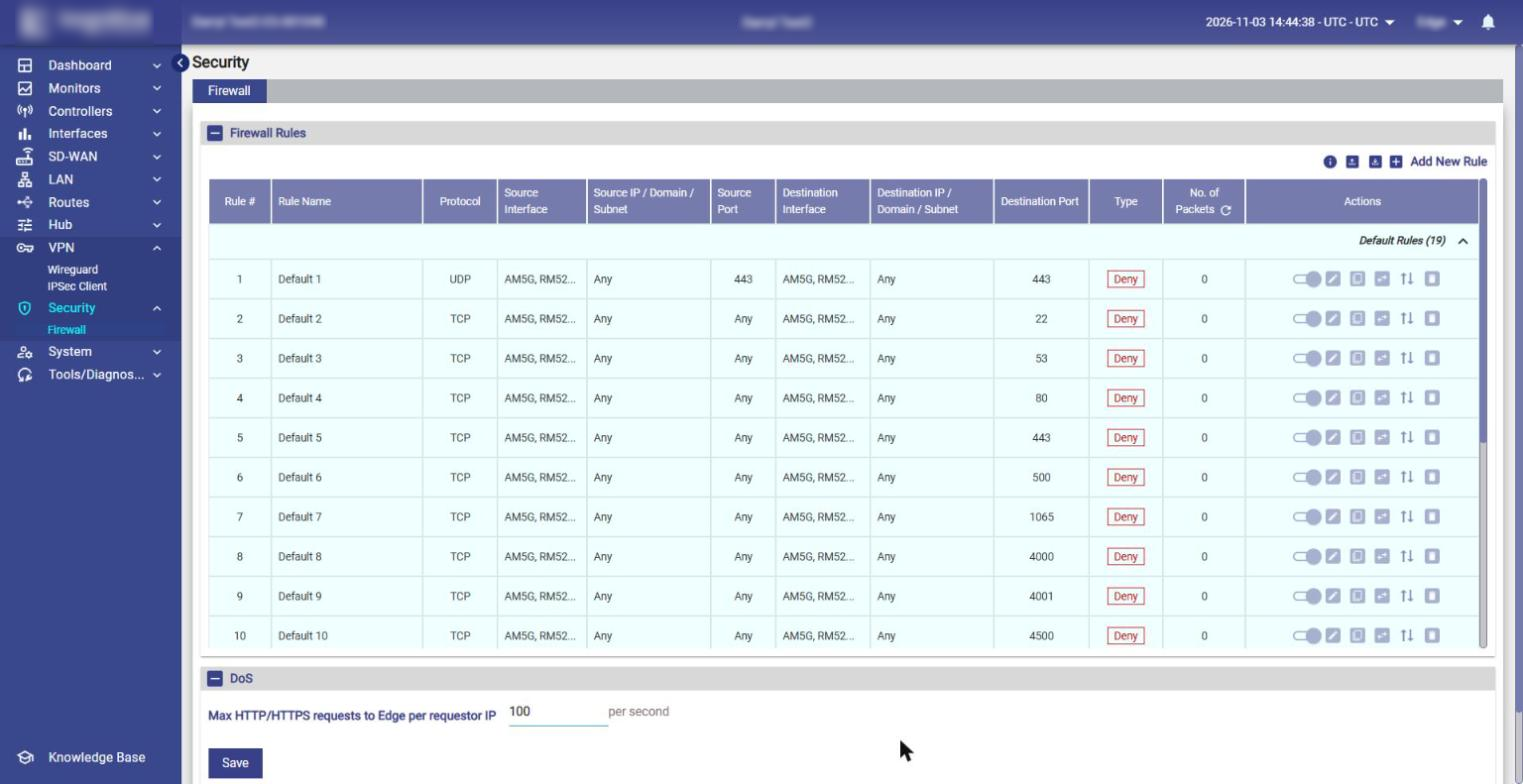
Firewall Rules table
The Firewall Rules table has the following columns: Rule #, Rule Name, Protocol, Source Interface, Source IP / Domain / Subnet, Source Port, Destination Interface, Destination IP / Domain / Subnet, Destination Port, Type (Allow/Deny), No. of Packets and Actions. By default, the highest priority is assigned to the top rule and the priority decreases down the list.
The following icons are available at the top right of the table:
-
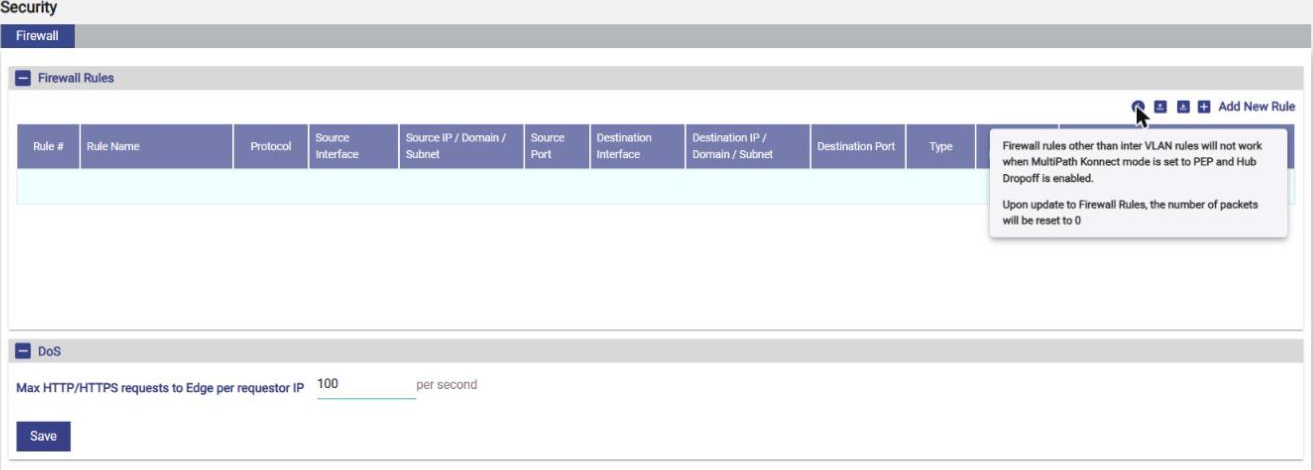
ℹ (Information) – point to it to view the notes about firewall rules, see Figure Firewall Rules Information.
-
Upload CSV – upload firewall rules from a CSV file, see section Adding Firewall Rules through CSV Template.
-
Download CSV – download the configured firewall rules as a CSV file.
-
Add New Rule – add a firewall rule, see section Adding a Firewall Rule.
The ℹ tooltip reads:
-
Firewall rules other than inter VLAN rules will not work when MultiPath Konnect mode is set to PEP and Hub Dropoff is enabled.
-
Upon update to Firewall Rules, the number of packets will be reset to 0.
Default Rules
The table starts with a collapsible Default Rules group (for example, Default Rules (19)). Click the arrow next to it to expand or collapse it. Default rules are system-defined Deny rules applied to the WAN interfaces that block inbound access to common service ports (for example, UDP 443 and TCP 22, 53, 80, 443, 500, 1065, 4000, 4001 and 4500). The Edit, Clone, Bi-Directional, Move and Delete icons of the default rules are disabled.
Actions
Each user-defined rule has the following icons in the Actions column:
-
Enable/Disable toggle – enable or disable the rule, see sections Disabling Firewall Rule and Enabling Firewall Rule.
-
Edit (pencil) – modify the rule.
-
Clone (copy) – create a copy of the rule.
-
Bi-Directional (arrows) – create the reverse rule, see section Creating Bi-Directional Rule.
-
Move (↑↓) – drag the rule to change its priority, see section Defining New Priority of the Firewall Rules.
-
Delete – delete the rule.
Adding a Firewall Rule
To add a firewall rule, perform the following steps.
-
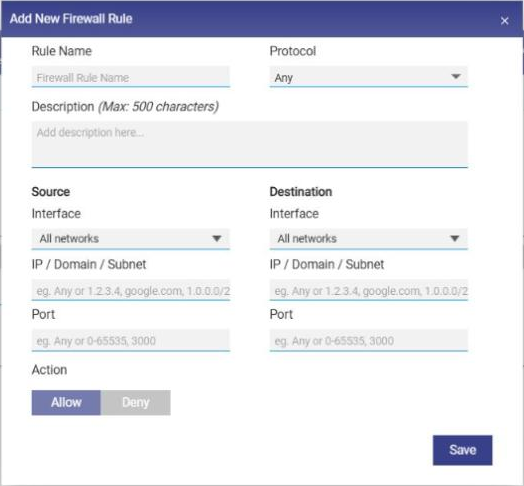
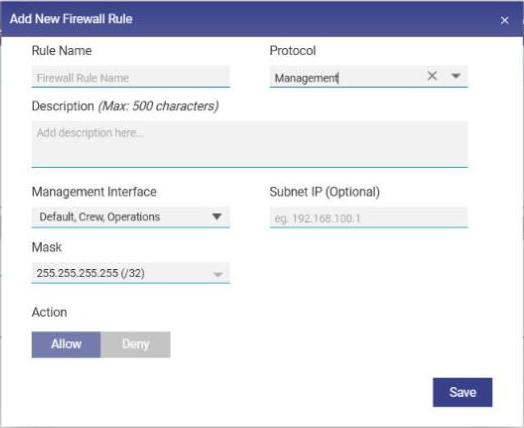
Click Add New Rule at the top right of the Firewall Rules table. The Add New Firewall Rule pop-up appears, see figure below.
-
Enter data in the respective fields, see Table Add New Rule.
-
Click Save. To close the pop-up without saving, click ×.
|
Fields |
Configuration |
|---|---|
|
Rule Name |
Enter a unique name for the rule. The name can include alphanumeric and special characters. |
|
Protocol |
Select the protocol to which the rule applies. By default, Any is selected. The list includes:
|
|
Description |
Optionally, enter a description of the rule (maximum 500 characters). |
|
Source – Interface |
Select the source interface(s) or network(s) to which the rule applies. By default, All networks is selected, which applies the rule to all WANs and networks. |
|
Source – IP / Domain / Subnet |
Enter the IP address, domain name or subnet of the source, or Any (for example, 1.2.3.4, google.com, 1.0.0.0/24). |
|
Source – Port |
Enter the source port(s): Any, a single port, a range or a comma-separated list (for example, 0-65535, 3000). |
|
Destination – Interface |
Select the destination interface(s) or network(s). By default, All networks is selected. |
|
Destination – IP / Domain / Subnet |
Enter the IP address, domain name or subnet of the destination, or Any. |
|
Destination – Port |
Enter the destination port(s): Any, a single port, a range or a comma-separated list. |
|
Action |
Click Allow (default) to allow the matching traffic, or Deny to block it. The selected action is shown in the Type column of the table. |
Table Add New Rule
When the Protocol is set to Management, the Source and Destination fields are replaced by the following fields:
-
Management Interface – the Access Network(s) from which management access is controlled.
-
Subnet IP (Optional) and Mask (default 255.255.255.255 (/32)) – the source address of the management traffic. The Management Interface, Subnet IP and Mask are stored as the Source IP / Subnet of the rule.
Adding Firewall Rules through CSV Template
The user can upload firewall rules in CSV format.
-
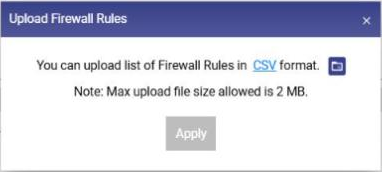
Click the Upload CSV icon at the top right of the Firewall Rules table. The Upload Firewall Rules pop-up appears, see figure below.
-
Click the CSV link to download the CSV template.
-
Open the template and enter the required details. The maximum upload file size is 2 MB.
-
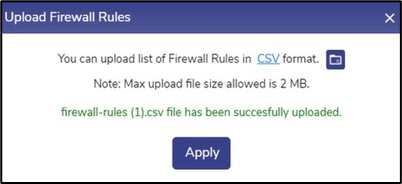
Click the Upload icon next to the CSV link and select the CSV file. The system validates the file and shows a success message.
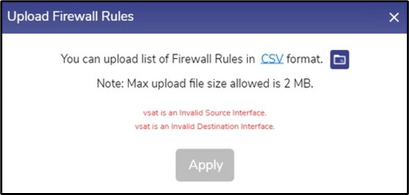
If the validation is not successful, the system shows the errors in the pop-up. Correct the errors in the CSV file and upload it again.
-
Click Apply (enabled after a file is uploaded) to apply the new firewall rules. This replaces the existing rules with the new set of firewall rules.
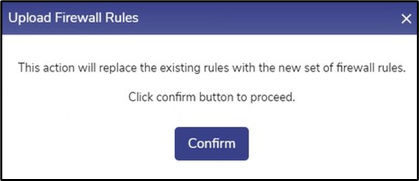
-
Click Confirm. The system validates the file again. Once the validation is successful, the rules are displayed in the Firewall Rules table.
If the validation is not successful, the errors are shown in the following pop-up. Correct the errors in the CSV file and upload it again.
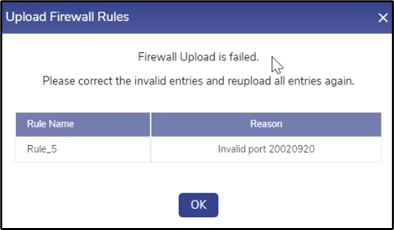
To export the configured rules, click the Download CSV icon.
Modifying Firewall Rule
-
Click the Edit (pencil) icon of the firewall rule to be modified. The edit pop-up appears, see figure below.
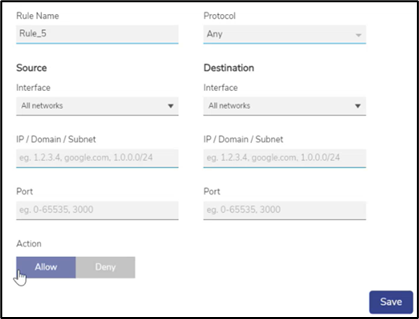
-
Modify the fields, see Table Add New Rule.
-
Click Save. The number of packets of the rules is reset to 0.
Disabling Firewall Rule
By default, a firewall rule is enabled.
-
Click the toggle switch of the firewall rule to be disabled. The Disable Firewall Rule pop-up appears, see figure below.
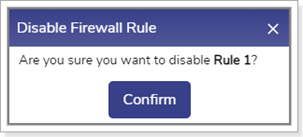
-
Click Confirm. The firewall rule is disabled.
Enabling Firewall Rule
-
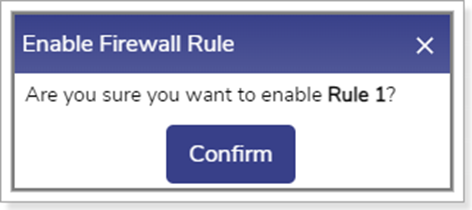
Click the toggle switch of the disabled firewall rule. The Enable Firewall Rule pop-up appears, see figure below.
-
Click Confirm. The firewall rule is enabled.
Deleting Firewall Rule
-
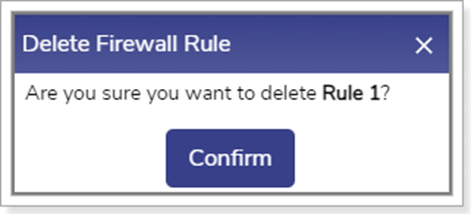
Click the Delete icon of the firewall rule to be deleted. The Delete Firewall Rule pop-up appears, see figure below.
-
Click Confirm. The firewall rule is deleted.
Defining New Priority of the Firewall Rules
-
Click and hold the Move (↑↓) icon of the firewall rule whose priority is to be changed.
-
Drag the rule to the required position in the list. Rules higher in the list have a higher priority.
Creating Bi-Directional Rule
-
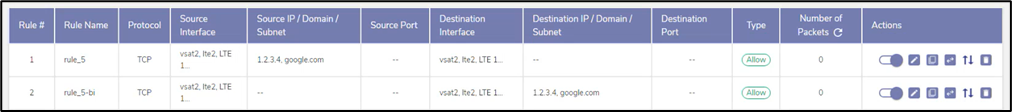
Click the Bi-Directional (arrows) icon in the Actions column of the rule.
-
The system creates a new rule in which the Source and Destination are swapped, with the name prefixed by "Bi".
Note: The Bi-Directional option is not applicable to firewall rules created with the Management protocol, because these rules have only source details and no destination details.
Resetting the Number of Packets
-
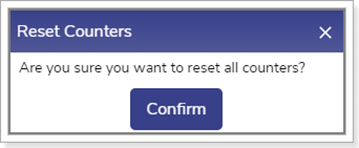
Click the Refresh (⟳) icon in the No. of Packets column header. The Reset Counters pop-up appears, see figure below.
-
Click Confirm. All packet counters are reset.
DoS
The DoS section protects the KonnectOS System against excessive HTTP/HTTPS requests, see Figure Firewall Rules Information and DoS.
-
Click + next to DoS to expand the section.
-
In Max HTTP/HTTPS requests to Edge per requestor IP, enter the maximum number of HTTP/HTTPS requests per second allowed from a single IP address to the KonnectOS System. The default value is 100 per second.
-
Click Save.
Firewall Reports
Note: Firewall Reports are available in the Kognitive Cloud portal, not on the KonnectOS System.
The Firewall activity can be viewed in real time using the Firewall Reports screen in Kognitive Cloud.
-
Login to Kognitive Cloud with valid credentials.
-
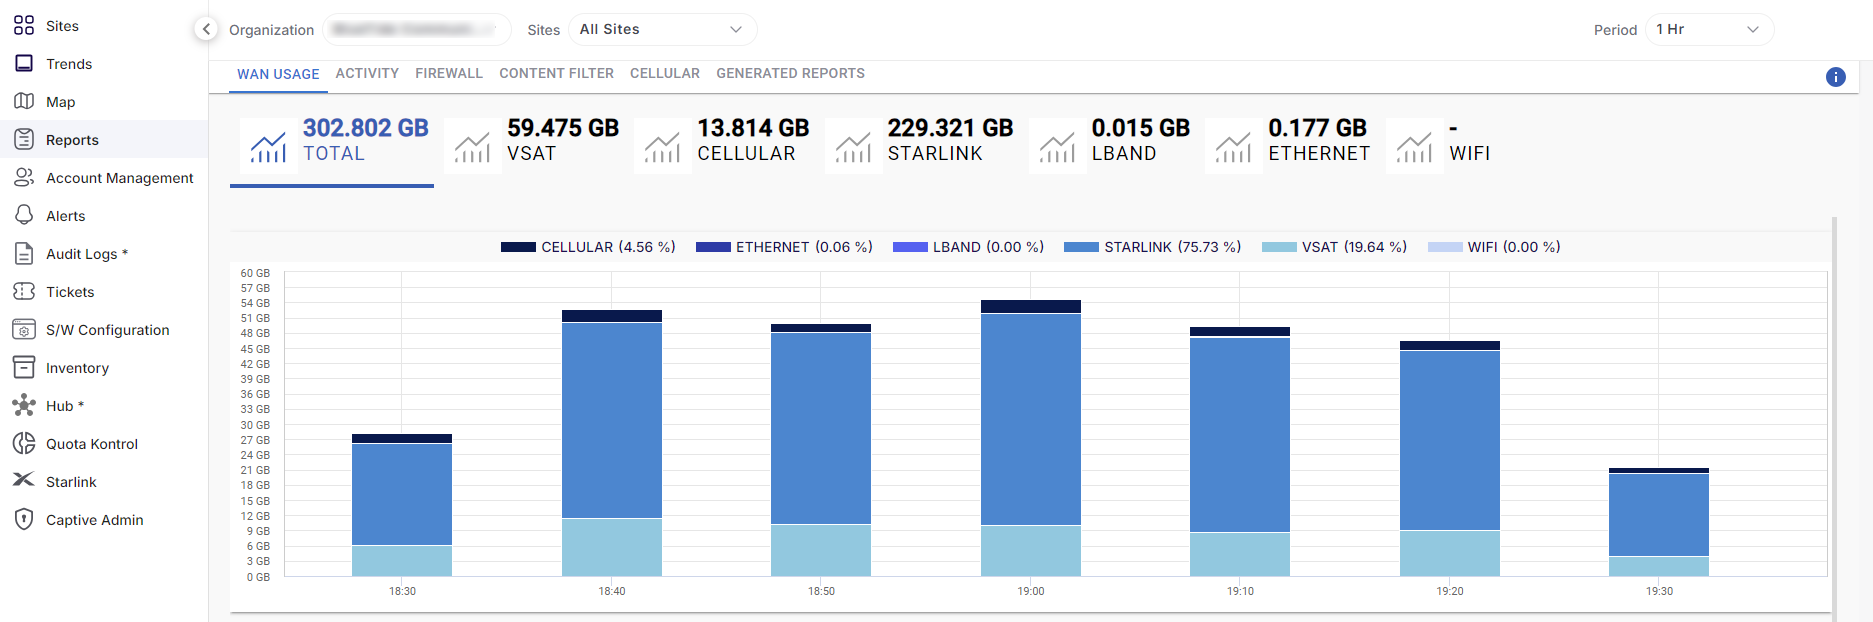
Select Reports from the left menu bar.
-
Click Firewall tab in the Reports screen.
-
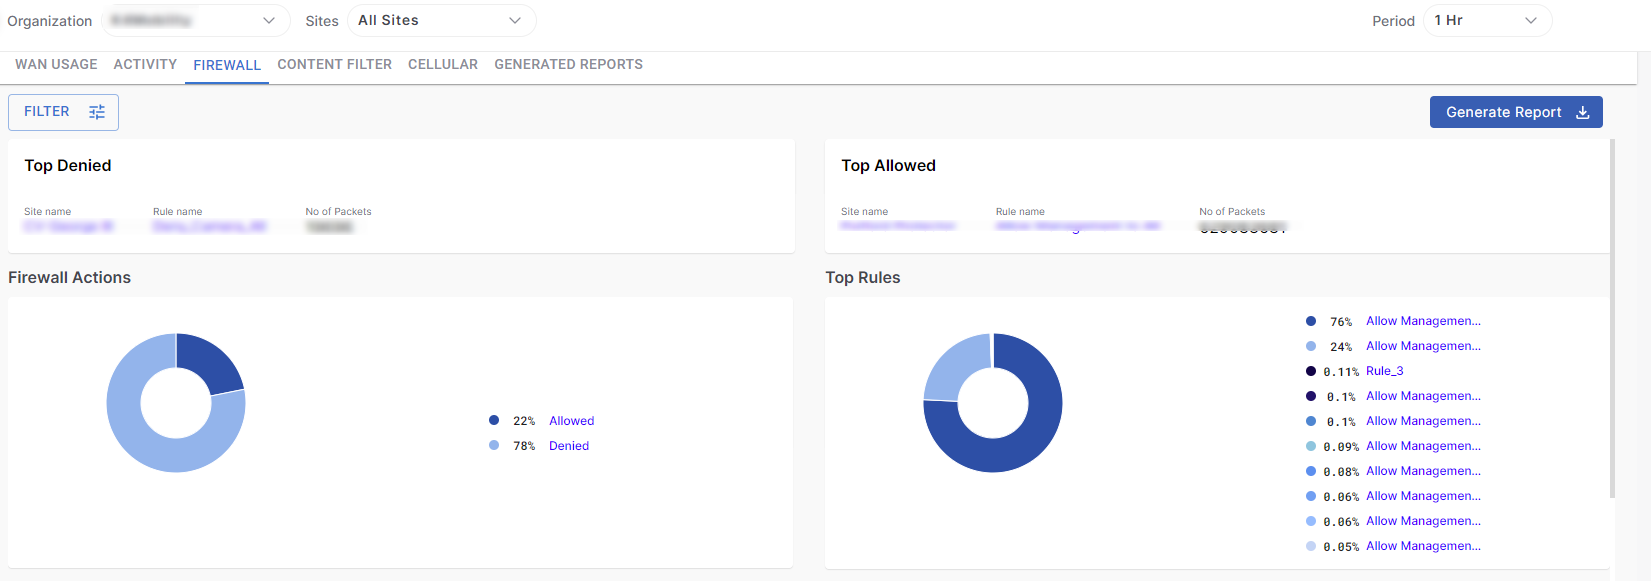
The Firewall tab enables the user to view reports about the Firewall rules set for the selected organization.
-
Users can view information such as:
-
The Top Denied rule
-
The Top Allowed rule
-
Percentage of allowed and denied rules
-
The most utilized rules
-
List of all rules set for the organization
-
-
In the Organization field, select the Organization or sub-organization from the dropdown menu. The logged in admin Organization is populated by default here. This is the organization corresponding to the email ID used to login.
-
The dropdown list consists of all the sub-organizations under logged in admin organization.
-
Select the Sites from the dropdown menu.
-
Select the Period from the dropdown menu.
-
By default, the time interval selected is last one hr. The user can also select a custom time interval using the From and To fields.
-
The Firewall tab shows the data as shown in the below figure.
-
Click the Generate Report button to download the Firewall reports in PDF format.
Headers
The headers show the following information:
-
Top Denied - The Firewall rule that was used to deny the maximum number of packets. The Site name and number of packets is also shown.
-
Top Allowed - The Firewall rule that was used to allow the maximum number of packets. The Site name and number of packets is also shown.

Firewall Actions
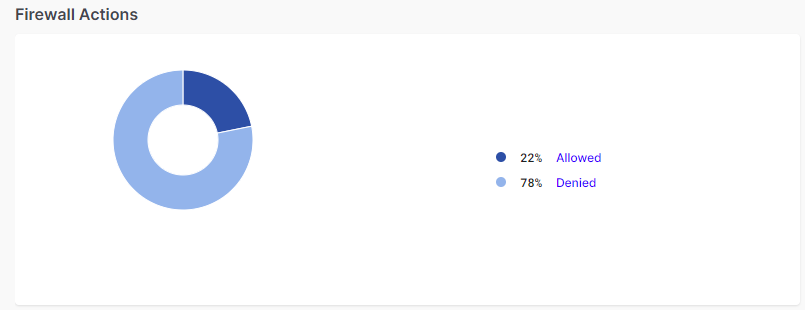
The Firewall Actions pie chart groups the firewall rules set by the users into Allowed and Denied categories and shows the percentage of each category. Hovering on any item on the pie chart highlights the category and shows number of rules in that category.
Top Rules
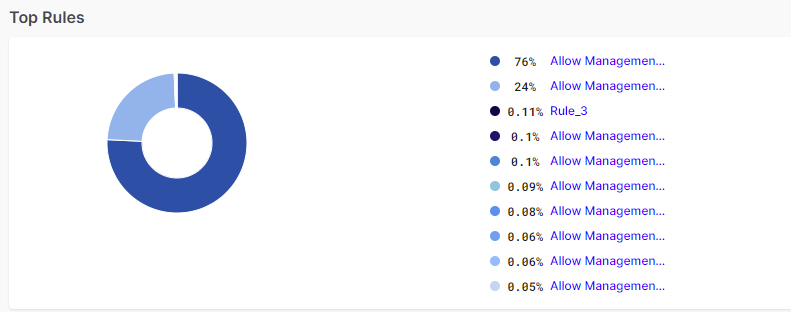
The Top Rules pie chart shows the most used Firewall Rules and shows their percentage. Hovering on any item on the pie chart highlights the category and shows number of packets in that category.
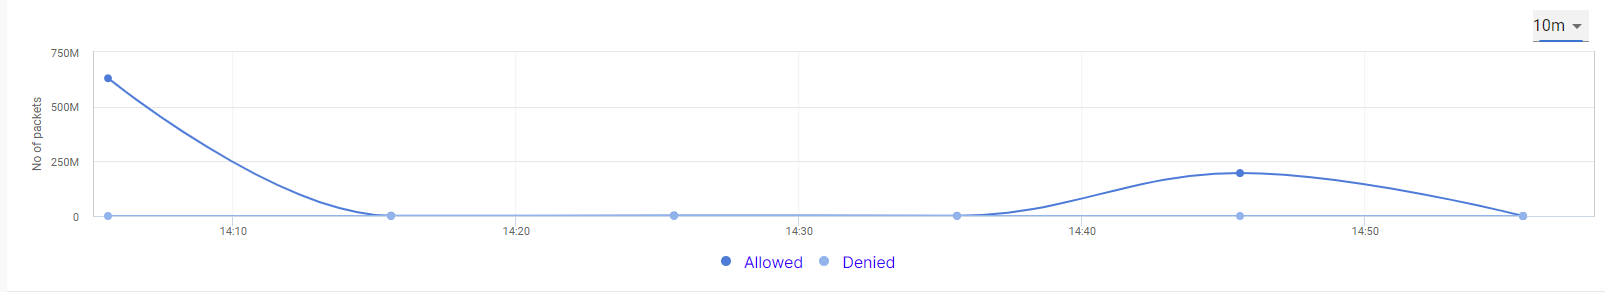
The line chart shows the amount of allowed and denied packets at different time instances. The horizontal axis contains the time instances, and the vertical axis contains the amount of packets. The graph between these two axes gives the user a clear understanding of how the firewall rules have been utilized over the selected time period.
Select the dropdown menu at the top right corner of the chart to change the time interval on the chart.
-
All the blue highlighted text in the Firewall screen is clickable. It can be the name of a site, name of a rule, or rule category. Clicking it filters the entire screen and displays the firewall rules information corresponding only to that site, rule, or rule category.
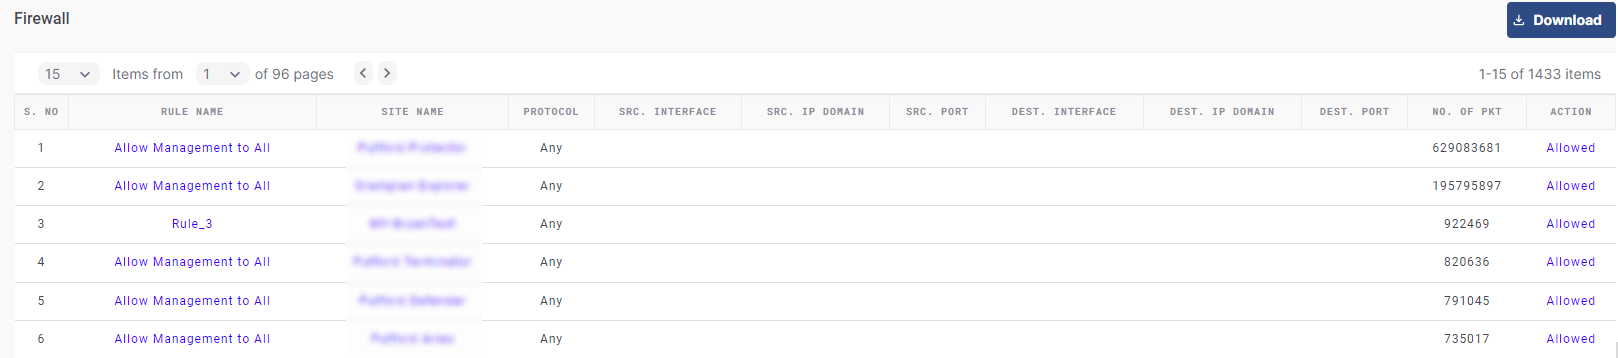
Firewall Table
The Firewall section shows a table that lists all the rules set under the selected organization. The Table shows the following information:
-
Rule Name - Name of the rule.
-
Site Name – Name of the Site.
-
Protocol
-
Source Interface
-
Source IP Domain
-
Source Port
-
Destination Interface
-
Destination IP Domain
-
Destination Port
-
No of Packets– Total number of packets used for the rule.
-
Action – Type of rule (Allowed/Denied)
Click the Download button to download the Firewall rules data locally in CSV format.